You sign up for a new shopping site and, because you’re in a hurry, you reuse the password you already use for your email. Cue six months later: that shop’s website gets breached, someone tries the same email and password on your other accounts, and your inbox, your bank, and your social profiles are all exposed from one lazy moment.
It might sound unlikely, but it’s actually how many account takeovers start. It’s also why the answer to what makes a password strong keeps shifting. Advice that felt solid a few years ago now looks dated, and some rules people still follow do very little.
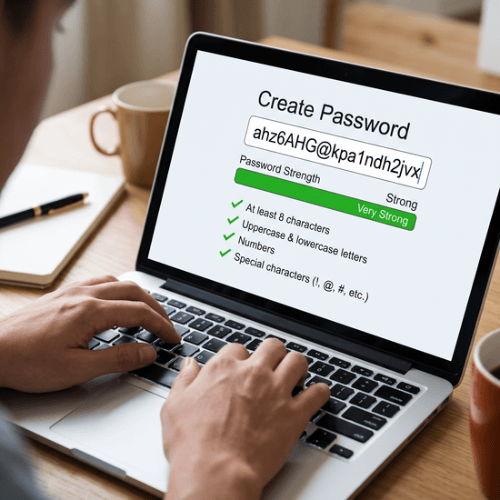
This guide covers what a strong password looks like today, where the usual advice goes wrong, and the simplest way to create one for every account you own.

A strong password is a long, random, unique set of characters, or a passphrase of several unrelated words, that is hard for a person or a cracking tool to guess and isn’t used on any other account.
Length does most of the work because each additional character multiplies the number of guesses an attacker must make. Therefore, a 16-character passphrase beats an 8-character mix of letters and symbols.
Then, uniqueness covers what length can’t. If one site is breached, a password that exists nowhere else is worthless to whoever stole it.
Unpredictability is the third piece. A password that follows a pattern, even a complicated-looking one, is easier to crack than a random string of the same length. After all, people are predictable, and cracking tools are built around that.
Together, those traits make a password hard to guess, hard to phish, and useless to anyone who finds it in a leaked database.

Four things decide how strong a password really is:
While character variety still helps, it ranks below length and uniqueness. “h3ll0w0rld$” looks tough and falls quickly, because those substitutions are the first ones cracking tools try. A 20-character passphrase of unrelated words usually takes far longer to break and is easier to remember.

Personal details are the other trap. Pet names, birthdays, and kids’ names are the first things anyone who knows you will try, and they turn up in social posts, breach data, and password reset questions.
A quick checklist before you save a password: at least 16 characters, used nowhere else, no personal clues, no pattern you could explain to someone else.
The difference between a weak and a strong password is rarely about how clever it looks.
| Approach | Example pattern | Why it fails or holds up |
|---|---|---|
| Personal details | Child's name plus a birth year | Easy to find online, tried first |
| Keyboard walk | qwerty12345 | Cracking tools include these sequences |
| Substitution | p@ssw0rd! | Letter swaps are in every cracking dictionary |
| Site twist | Amazon2024! | Site name plus a year is a known pattern |
| Long passphrase | Four unrelated words, 16+ characters | Long, random, not in any dictionary |
| Generated string | 20 mixed characters | No pattern to exploit, impossible to memorize |
Weak passwords share a shape or pattern. They come from something about you or something about the keyboard.
Attackers don’t guess one password at a time. They run lists of leaked passwords, common words, and known substitutions, then try the same list across thousands of accounts.
Reusing passwords is the mistake that turns a small breach into a big one. When a site leaks its user database, the email and password pairs often end up for sale, and attackers test them on email providers, banks, and social networks within hours.
Use that password in five places and one breach becomes five compromised accounts, with reset emails landing in an inbox someone else may already be reading.
The fix is simple: a long, random password that exists only once.
Start with length: 16 characters at minimum, and longer for email, banking, and anything that can reset your other accounts.
Remove personal clues, so nothing on your social profiles and nothing a friend could guess ends up inside it.
Keep every password unique, which is the rule that matters most after a breach and the hardest one to follow by hand once you have more than a dozen accounts.
A password generator handles the random part and removes the temptation to invent something memorable, which usually means something guessable. You can see what a strong one looks like with our free password generator.
That’s where a password manager earns its keep. It generates long passwords, stores them in an encrypted vault, fills them in at login, and flags the weak or reused ones you’ve been carrying for years.
You memorize one password, and it handles the rest. Our guide to the best password managers covers what separates a good one from a basic one.
LastPass is one example: a built-in generator, autofill on desktop and mobile, and a security dashboard that points out weak, reused, and compromised passwords.
LastPass remains one of the best-known password managers on the market, offering practical features like autofill, password sharing, dark web monitoring, and support across major devices and browsers.
While the 2022 breach is still an important part of the company's history, more recent developments have focused on rebuilding trust through stronger security and product updates. These include separating from its parent company, hardening its infrastructure, raising master password security standards, expanding encryption measures, and rolling out newer capabilities like passkey support.
LastPass's core features were never in doubt, since it offers all elements necessary for excellent password management, such as a password generator, password sharing, dark web monitoring, and autofill. Additionally, there's a free version with unlimited password storage, free trials for all plans.
Passkeys deserve a mention too. Some accounts now let you sign in with a fingerprint or your face instead of a password, and where they work, they’re safer than any password. They don’t cover everything yet, and a strong master password still protects the vault behind them.
Most people don’t need a perfect system. They need a few habits that hold up: long passwords, one per account, no personal information in them, and a password manager to do the remembering.
Start with the accounts that would hurt most to lose: usually email, banking, and anything with a saved card. Change those first, then work through the rest as you log in.
If your passwords are still in your head, in a notes app, or on paper, it’s time to move them. Password managers like LastPass can generate and store strong passwords for you, so the only one you need to remember is the one that gets you in.
At least 16 characters. Length matters more than complexity, because every extra character makes guessing harder. For email, banking, and your password manager, 20 characters or a passphrase of four or more unrelated words is a safer target.
A long passphrase of random unrelated words is usually as strong as a random string of similar length, and much easier to remember. The randomness is what counts. Four words that form a sentence are far weaker than four words with no connection to each other.
Yes. Most password managers include a generator that creates long random passwords or passphrases and saves them to your vault. That removes the two usual weak spots: passwords derived from personal information and passwords reused across accounts.
Not yet. Passkeys are available on many major services and better resist phishing than passwords, but many accounts, older devices, and recovery flows still rely on passwords. Most people will use both for a while.
Change a password when there is a reason: a breach, a suspicious login, or a device someone else used. Forced changes every few months tend to push people toward weaker, predictable variations, so current guidance favors long, unique passwords and changes only when needed.
Share your thoughts, ask questions, and connect with other users. Your feedback helps our community make better decisions.
©2012-2026 Best Reviews, a clovio brand –
All rights
reserved